
ShieldLabs
Contact
ShieldLabs
A fraud and abuse detection platform that identifies risky visitors, shared accounts, multi-accounting, and suspicious traffic.
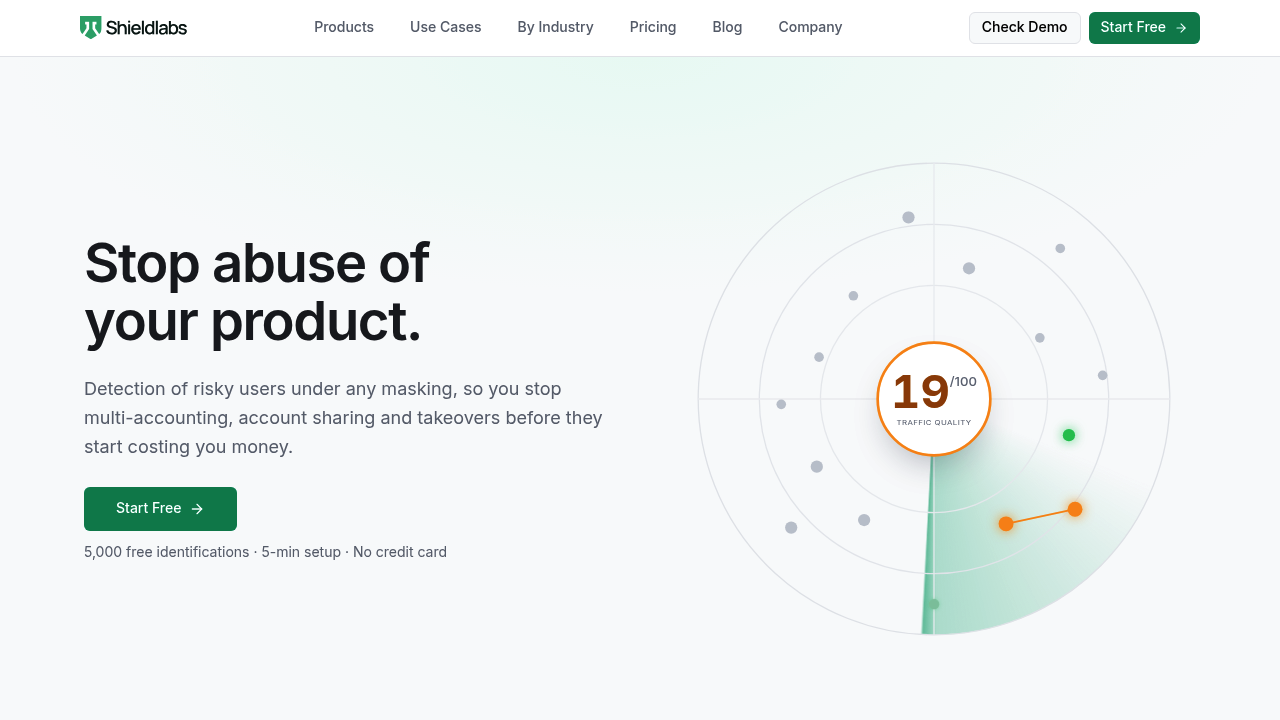
ShieldLabs is a fraud and abuse detection platform designed to help online businesses identify risky visitors and suspicious account activity. It analyzes device, browser, network, and traffic signals to recognize visitors and assign a risk score, helping businesses separate legitimate users from potentially abusive activity.
The platform can detect common problems such as multi-accounting, account sharing, account takeovers, free trial abuse, promo abuse, and fraudulent advertising traffic. It can recognize returning visitors even when cookies have been cleared, IP addresses have changed, or incognito mode is being used. High-risk events can also connect accounts, devices, and IP addresses to uncover patterns of abuse.
ShieldLabs analyzes more than 300 signals, including VPN and proxy use, datacenter IP addresses, browser automation, anti-detect browsers, location information, and suspicious paid clicks. Each visitor receives an explainable risk score along with the signals behind it, allowing businesses to decide how different levels of risk should be handled instead of relying on a hidden scoring system.
The service is built for developers and can be added to a website with a JavaScript snippet. It also provides API and webhook access for connecting risk information with existing systems and workflows. Along with fraud detection, ShieldLabs includes traffic analytics that help businesses understand traffic quality, identify suspicious acquisition sources, and get a clearer picture of their real users.
Categories
- All
-
 Advertising
-
 AI Agents
- AI Companions
-
 AI Wrappers
-
 AI Writing
-
 Analytics
-
 Art Generator
-
 Audio Editing
-
 Automation
-
 Brand Monitoring
- Branding
-
 Business Tools
-
 Chatbots
-
 Code Assistant
-
 Content Marketing
-
 Customer Support
-
 Design Generators
-
 Developer Tools
-
 Directories
- Document Management
-
 Education
-
 Email Marketing
-
 Fashion
- Finance
- Fitness
- Gift Ideas
- Image Editing
- Image Generators
- Logo Generators
- Low-Code/No-Code
- Marketing
- Music
- Personal Assistant
- Podcasting
- Productivity
- Project Management
- SEO
- Social Media
- Stock Photos
- Text to Image
- Text to Speech
- Text to Video
- Transcription
- Translator
- Video Editing
- Video Enhancer
- Video Generators
- Website Builders
- Workflows